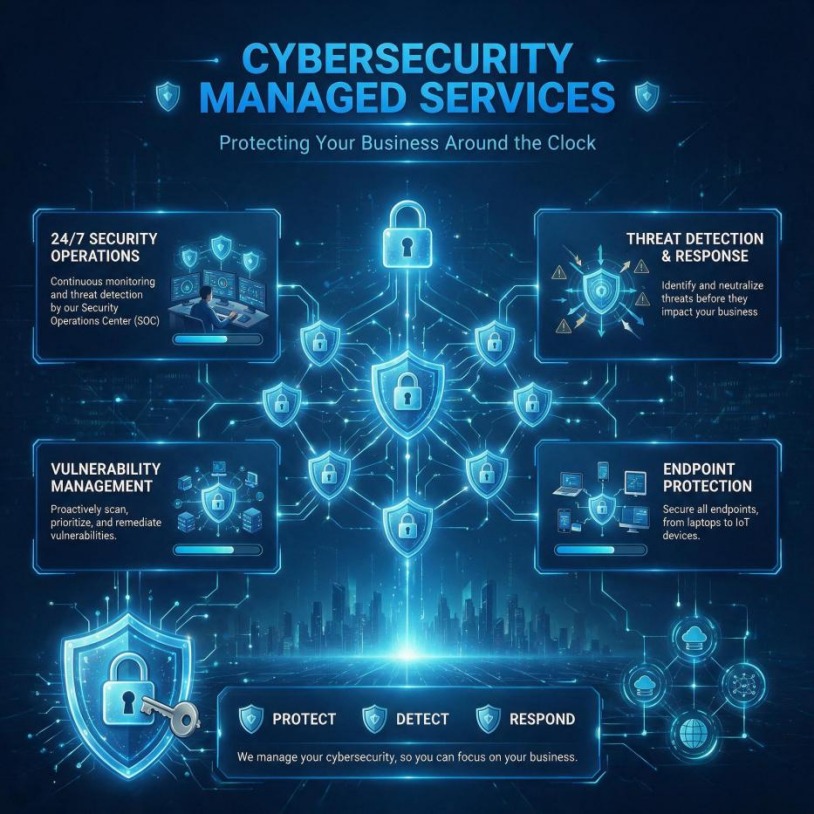
Cyber threats don't work office hours — and neither do we. Intrinsic Security's Managed Services give your organization a dedicated, 24/7 security operation without the cost and complexity of building one in-house. From continuous threat monitoring and detection to vulnerability management and incident response, our certified analysts and industry-leading technology platforms work around the clock to protect your infrastructure, data, and reputation — so your team can focus on running the business.
Expert security monitoring, detection, response and protection for modern enterprises.
24/7 monitoring, alert triage, investigation and response.
Continuous security analytics, monitoring and threat investigation.
Advanced detection, investigation and rapid threat response.
Vulnerability assessment and penetration testing.
Infrastructure monitoring, performance and operational response.
Managed endpoint, identity, email and cloud protection.
Protection against credential theft, privilege abuse and identity attacks.
Firewall, segmentation, VPN and network security management.
Cloud posture monitoring, configuration and risk management.
Continuous monitoring and protection for industrial environments.
Digital forensics, incident response, investigation and recovery.
Proactive investigation to uncover hidden attacker activity.
A complete, modular suite of managed security services — built to scale with your organization and aligned to regional compliance requirements.
What it is: A dedicated team of security analysts monitoring your environment 24/7/365, triaging alerts, investigating anomalies, and escalating real threats before they become incidents.
What's included:
Technology: Microsoft Sentinel, Elastic SIEM, Wazuh, IBM QRadar
What it is: Our security team operates the client-licensed SIEM, managing rules, tuning, triage and escalation while the client retains the platform and security data.
What's included:
Technology: Microsoft Sentinel, Splunk Enterprise Security, Elastic SIEM, IBM QRadar, Google Chronicle/SecOps, Wazuh
What it is: MDR bundles detection technology, security platform capabilities and analyst services into a single managed subscription, providing continuous detection, investigation and response.
What's included:
Technology: CrowdStrike Falcon, SentinelOne Singularity, Microsoft Defender XDR
What it is: Vulnerability Assessment and Penetration Testing identifies exploitable weaknesses across infrastructure, applications and cloud environments through assessment and controlled security testing.
What's included:
Technology: Tenable/Nessus, Qualys, Burp Suite, Metasploit
What it is: A dedicated Network Operations Center focused on infrastructure availability, performance monitoring and operational incident management. NOC services are distinct from, but complementary to, security monitoring.
What's included:
Technology: Client network infrastructure and operational monitoring platforms
What it is: Managed endpoint and extended detection across endpoint, identity, email and cloud environments, providing continuous visibility and response against sophisticated threats.
What's included:
Technology: CrowdStrike Falcon, SentinelOne Singularity, Microsoft Defender XDR, Palo Alto Cortex XDR, Trend Micro
What it is: Identity Threat Detection and Response monitors identity and IAM telemetry to identify credential theft, token hijacking, MFA abuse, privilege escalation and lateral movement.
What's included:
Technology: Microsoft Defender for Identity, CrowdStrike Falcon Identity, SentinelOne Singularity Identity, Silverfort, Varonis, Semperis, Permiso
What it is: Managed network security covering next-generation firewall policy management, segmentation, WAF, VPN and Zero Trust Network Access with continuous monitoring.
What's included:
Technology: Palo Alto, Fortinet, Check Point, Cisco
What it is: Continuous cloud security monitoring that detects cloud misconfigurations, compliance drift and identity or entitlement risks across multi-cloud environments.
What's included:
Technology: Wiz, Palo Alto Prisma Cloud, Microsoft Defender for Cloud, CrowdStrike Falcon Cloud Security
What it is: Passive, protocol-aware security monitoring designed for operational technology and industrial control environments where traditional endpoint agents may not be suitable.
What's included:
Technology: Dragos, Claroty, Nozomi Networks, Microsoft Defender for IoT, Tenable OT, Armis, TXOne
What it is: Retainer-based breach response covering containment, forensic imaging and analysis, root-cause investigation and regulatory-notification support when a security incident occurs.
What's included:
Technology: Industry-standard digital forensics and incident-response toolsets